Attackers using AI

Threat actors using AI models, agents or AI-built tooling to plan, scale or run offensive operations. Each entry is a short summary with a direct link to the original report or article.

175 entries, last updated 10 Nov 2026, 20:19 UTC. All entries.

Added 10 Nov 2026

  1. RailwayVendor report

    Incident Report: October 21st Security Attack (opens blog.railway.com)

    Railway reports an intrusion in which the attacker used AI agent fanouts, reportedly abliterated models in an ARTEX-like harness per Wiz, to find exploits and move laterally. They stole and decrypted environment variables, mainly AI provider keys, from up to 1.85% of workspaces. Estimated unauthorized spend on the stolen keys was about $740,000.

    Category
    AI-Enabled
  2. Okta Threat IntelligenceVendor report

    Agentic attack tools accelerate reconnaissance of identity flows (opens okta.com)

    Okta Threat Intelligence assesses that multiple actors tasked agentic frameworks, likely the ARTEX multi-agent penetration testing framework, with large-scale reconnaissance, fraudulent registration, credential stuffing and OAuth flow probing against hundreds of Auth0 and Okta tenants. Some activity overlaps with Storm-0940. No novel exploitation was seen, and Okta could not confirm ARTEX use for all activity.

    Category
    AI-Enabled
    Malware
    ARTEX
    Attribution
    China, per Microsoft (confidence not stated)
  3. Securelist (Kaspersky)Vendor report

    Mobile threat report for Q3 2026 (opens securelist.com)

    Kaspersky's Q3 2026 mobile report notes an Android app posing as Google Play Protect that used the DistilBERT model to interpret C2 commands, and a banking Trojan that classified gallery images with an on-device AI model to find card data. Most of the report covers general mobile malware statistics.

    Category
    AI-Enabled

Added 9 Nov 2026

  1. GitGuardianVendor report

    Beyond ARTEX: 45 AI Pentesting Tools and How to Find Them (opens blog.gitguardian.com)

    GitGuardian catalogs about 45 open-source frameworks that wire an LLM agent into a loop running offensive tools, following the ARTEX takedown. Four ship a secret scanner wired to the agent, though none has a GitHub fetcher. Shodan fingerprinting found many exposed operator consoles, 1,428 services for the ARTEX family alone.

    Category
    AI-Enabled
  2. Datadog Security LabsResearch

    On the hunt for ARTEX: understanding agentic attacks in AWS environments (opens securitylabs.datadoghq.com)

    Datadog observed attackers using ARTEX, an AI-native penetration framework where LLM agents plan and run attacks, against AWS environments in October 2026. It used compromised IAM keys to search CloudWatch logs for financial data and secrets, and abused public Cognito user pools. The post lists IPs, user agents and detection rules.

    Category
    AI-Enabled
    Malware
    ARTEX
    Attribution
    China, per Microsoft (confidence not stated)
  3. The Hacker NewsNews

    CERT-In Flags AI-Driven Attacks as Backdoored ARTEX Exposes 62 Consoles to Root Access (opens thehackernews.com)

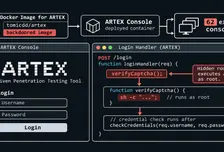
    CERT-In says a threat actor it tracks as Crafty Falcon is using public AI offensive tools (ARTEX, PentAGI, Cairn, CyberStrikeAI) to run autonomous attack chains against Indian BFSI and crypto targets. Separately, a copycat ARTEX Docker image with a hidden unauthenticated root shell was served from 62 consoles, and downloaded 9,000 times.

    Category
    AI-Enabled

Added 8 Nov 2026

  1. Malbear LabsResearch

    Operation Snowball: Inside an Autonomous AI Intrusion Campaign (opens malbearlabs.com)

    A jailbroken DeepSeek Flash agent, run through a custom autonomous harness, carried out two weeks of largely unsupervised intrusion activity against a European telecoms provider and thirteen hosted organizations. An exposed open directory held about 70 session transcripts, a Chinese-language jailbreak prompt, skill modules and a scoring rubric.

    Category
    AI-Enabled

Added 7 Nov 2026

  1. Microsoft Security BlogVendor report

    ARTEX abuse expands as cybercriminals target financial sector (opens microsoft.com)

    Storm-3358, a Cambodia-based financially motivated cluster, used the agentic AI offensive framework ARTEX against financial organizations from October 2026. ARTEX agents scanned and exploited web flaws such as anonymous file upload and SSRF, then dropped open-source RATs for persistence and lateral movement. Microsoft supplies behavioral signals, detections and IOCs.

    Category
    AI-Enabled
    Attribution
    Cambodia, per Microsoft Threat Intelligence (confidence not stated)

Added 6 Nov 2026

  1. Hunt.ioResearch

    Inside the PHP2Shell Arsenal: A Complete Dissection of a PAN-OS Mass-Exploitation Open Directory (opens hunt.io)

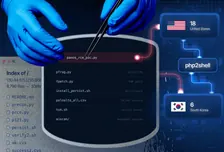
    An operator's exposed server held a PAN-OS exploitation toolkit and aiscan, a multi-agent AI penetration testing platform driven by DeepSeek and Kimi models. The session log shows DeepSeek v4-pro reading offensive playbooks and downloading tools on its own. The toolkit rooted 25 appliances. Claude Code was installed but not shown in use.

    Category
    AI-Enabled
  2. Microsoft Security BlogVendor report

    Threat actors use agentic AI tooling to find and abuse exposed secrets (opens microsoft.com)

    Threat actors used an agentic AI offensive framework, ARTEX, to search public GitHub repositories for exposed secrets, including AI service API keys, then abuse them in Entra ID and Azure. In one case an agent went from GitHub scanning to Azure Key Vault exfiltration in five minutes.

    Category
    AI-Enabled
    Malware
    ARTEX

Added 5 Nov 2026

  1. CensysResearch

    ARTEX: Agentic Asbestos (opens censys.com)

    Censys analysed ARTEX, an open-source LLM-driven autonomous penetration testing framework that CrowdStrike and Microsoft tied to attacks on South Korean finance and ConnectWise tenants. Censys counted 1,465 exposed ARTEX consoles, about 815 distinct deployments, 155 of them alongside other C2 or AI attack tools, and 32 open directories leaking attacker kits.

    Category
    AI-Enabled
    Attribution
    China, per Microsoft (confidence not stated); China, per CrowdStrike (medium confidence)
  2. 404 MediaNews

    The Confessions of an AI Fraud Kingpin (opens 404media.co)

    OnlyFake, a fraud service run by Yuriy Nazarenko, used AI-generated faces and backgrounds to produce realistic fake ID photos at scale for about $15 each, aimed at defeating KYC checks. The DOJ says it made $1.2 million from at least 10,000 IDs. The article also covers use by North Korean IT workers.

    Category
    AI-Enabled
    Malware
    OnlyFake
  3. Check Point ResearchResearch

    Hacking on Autopilot: Inside ARTEX Cybercrime Campaigns (opens research.checkpoint.com)

    Criminals are running the ARTEX agentic hacking platform, where LLM agents (mostly Chinese models such as DeepSeek Flash) autonomously find and exploit web vulnerabilities. Check Point found 1,608 live exposed instances and analysed 10 leaked databases. Campaigns included stealing iOS signing certificates and a failed crypto-draining effort, with minimal operator input.

    Category
    AI-Enabled
  4. WorkOSVendor report

    October 30th, 2026 Data Security Incident (opens workos.com)

    WorkOS disclosed that attackers used an AI-assisted offensive security framework to automate reconnaissance and exploitation against an internal sales application. CRM and support data was accessed, including contact details and customer communication summaries. WorkOS reports no evidence that production services or application data were affected. The investigation is ongoing.

    Category
    AI-Enabled

Added 4 Nov 2026

  1. Acronis Threat Research UnitVendor report

    BOSSAI: Inside the AI attack mesh that targeted Taiwan's emergency services (opens acronis.com)

    A single operator ran BOSSAI, a mesh of 12 AI agents (Hermes, OpenClaw, Cursor, Claude Code and others) with offensive MCP servers and abliterated local LLMs, to attack hundreds of organizations in eleven countries. Confirmed breaches at universities and emergency services led to medical data and PII theft. Commercial models often refused offensive tasks, and agents made frequent errors.

    Category
    AI-Enabled
    Actor
    BOSSAI
  2. Group-IBVendor report

    Weaponized AI: Inside the criminal ecosystem fueling the fifth wave of cybercrime (opens go.group-ib.com)

    Group-IB's white paper describes criminals using dark LLMs, deepfake-as-a-service, AI phishing and malspam tools, and AI-assisted RATs and stealers, based on dark web research. It reports a 371% rise in first posts with AI keywords (2019 to 2025) and subscription pricing from about $30 per month. It frames AI as a fifth wave of cybercrime.

    Category
    AI-Enabled
  3. Hunt.ioResearch

    ARTEX Exposed: Mapping the Infrastructure Behind the South Korean Bank Breaches (opens hunt.io)

    Attackers used ARTEX, an AI-driven autonomous penetration testing framework, with Claude Code routed to DeepSeek, GLM and Grok models, to breach South Korean financial institutions. Hunt.io found an open directory on a Hong Kong jump server holding model-routing shims, 19 agent skills, credentials and exploitation tooling, which widens the known infrastructure.

    Category
    AI-Enabled
    Attribution
    China, per CrowdStrike (medium confidence)

Added 3 Nov 2026

  1. BitdefenderVendor report

    3AM Hits European Schools: A Hybrid AI Ransomware Attack, Part Human, Part Agentic Loop (opens bitdefender.com)

    A 3AM ransomware affiliate breached a UK school estate in an operation Bitdefender assesses as hybrid: a human set goals while a language model appears to have run an agentic loop for repetitive commands and retries. The model and loop are inferred from command content and retry timing, not directly observed. Tooling was living-off-the-land plus public tools.

    Category
    AI-Enabled
    Actors
    3AM, ThreeAM
  2. Nextron SystemsVendor report

    Beyond Framework Signatures: Understanding AI-Driven Intrusions (opens nextron-systems.com)

    Nextron Systems analyzes ARTEX and Cairn, open-source autonomous penetration-testing frameworks that use LLM-driven agents to plan, execute and adapt intrusions with minimal human direction. It argues these frameworks complicate behavioral attribution since interchangeable models, prompts and tools can make different actors look alike or the same actor look different, while offering limited but real detection

    Category
    AI-Enabled
    Malware
    ARTEX, Cairn, Norma
  3. Unit 42Vendor report

    Unit 42 Threat Intelligence Highlights - Nov. 2, 2026 (opens unit42.paloaltonetworks.com)

    Unit 42 reports threat actors increasingly integrating generative AI and LLMs into offensive workflows, including generating tailored phishing lures and synthetic personas, assisting with scripting and code obfuscation, and using deepfakes for executive impersonation. The bulletin is a general roundup of observed trends across espionage and cybercrime rather than a single documented incident.

    Category
    AI-Enabled

Added 2 Nov 2026

  1. Unit 42Vendor report

    ARTEX Agentic AI Framework Used to Abuse Exposed APIs and Probe Identity Providers (opens github.com)

    Unit 42 observed intrusions using ARTEX, an openly released autonomous multi-agent AI penetration-testing framework whose planner agent, backed by an LLM, directs worker tools like nmap, nuclei and ffuf against targets.

    Category
    AI-Enabled
    Malware
    ARTEX, Sub2API
  2. CensysVendor report

    Thoughts on Vulnerability Response in the Era of the Vulnpocalypse and PHP2Shell (opens censys.com)

    Censys discusses how AI is lowering the cost and time barrier for turning obscure vulnerabilities into working exploits, citing PHP2Shell, two critical PHP memory-corruption bugs that required unusually complex research to exploit until AI tooling helped.

    Category
    AI-Enabled
  3. RST CloudResearch

    Tempo, not technique: hunting the AI harnesses behind today's intrusions (opens rstcloud.com)

    RST Cloud profiles three open-source agentic AI pentest harnesses, Cairn, ARTEX and PentAGI, which threat actors including Storm-0940 and VAPOR PANDA used to autonomously scan, exploit and move laterally across thousands of targets, reaching privileged cloud access within hours.

    Category
    AI-Enabled
    Attribution
    China, per CrowdStrike (confidence not stated); China, per VULONE (confidence not stated)
  4. Check Point ResearchVendor report

    2nd November - Threat Intelligence Report (opens research.checkpoint.com)

    Check Point's weekly bulletin reports the GOLD OGRE ransomware group using AI agents for reconnaissance and lateral movement during Aur0ra attacks, expanding AI adoption by North Korean threat actors, and China-linked VAPOR PANDA using the AI-enabled ARTEX framework against 200+ organizations with the BLOODALCHEMY backdoor.

    Category
    AI-Enabled
    Attribution
    North Korea, China, per not stated (confidence not stated)
  5. Kaspersky SecurelistVendor report

    CyberStrikeAI attacks educational institutions (opens securelist.com)

    Kaspersky identified a campaign using CyberStrikeAI, an open-source framework where an LLM orchestrator on the C2 server plans actions and generates commands executed by a non-AI implant on compromised hosts. Attackers used it against education-sector victims in Africa and Latin America, automating post-exploitation stages including persistence, discovery, lateral movement and credential dumping.

    Category
    AI-Enabled

Added 1 Nov 2026

  1. ProferoVendor report

    One Operator, Several AI Attack Agents: The Ultra Suite and ARTEX (opens profero.io)

    Profero describes a single threat operator using multiple AI-driven attack agent toolkits, including an 'Ultra Suite' and a tool called ARTEX, to automate offensive operations. The piece links to related AI attack agent projects such as CyberStrikeAI and VulnHunter, suggesting a broader ecosystem of AI-assisted hacking platforms. Full technical detail was not available in the retrieved text.

    Category
    AI-Enabled

Added 31 Oct 2026

  1. Cisco TalosVendor report

    Appraisal by AI: Model-driven victim prioritization in the VOLTA infostealer (opens blog.talosintelligence.com)

    Cisco Talos documents VOLTA, a Windows infostealer that sends stolen credentials, session tokens and personal data to LLMs via OpenRouter (Claude, Kimi, Gemini) to produce a ranked victim monetization and OPSEC dossier. The malware includes a multi-model fallback chain to bypass refusals and is sold as a builder, meaning any buyer gets AI-driven target triage.

    Category
    AI-Enabled

    Also covered byCisco Talos

Added 30 Oct 2026

  1. SophosVendor report

    AI used in Aur0ra ransomware testing and execution (opens sophos.com)

    The GOLD OGRE threat group used Cursor's Composer agent along with AI models from Anthropic, xAI, and Moonshot to test EDR evasion and orchestrate Aur0ra ransomware intrusions, bypassing AI guardrails by framing attacks as authorized red team activity.

    Category
    AI-Enabled
    Attribution
    Russia, per Sophos (low confidence)
  2. CrowdStrikeVendor report

    VAPOR PANDA Uses AI-Driven ARTEX to Scale a Global Espionage Campaign (opens crowdstrike.com)

    CrowdStrike reports that China-nexus actor VAPOR PANDA used the agentic AI framework ARTEX, powered by DeepSeek and a second commercial LLM, to run parallel intrusions against over 200 organizations across 14 countries.

    Category
    AI-Enabled
    Attribution
    China, per CrowdStrike (medium confidence)
  3. Group-IBVendor report

    Deepfake Fraud Prevention: Why Detection Alone No Longer Works (opens group-ib.com)

    Group-IB documents how attackers use AI-generated deepfake faces, voices and documents to defeat KYC, liveness checks and biometric authentication at scale, citing $5 synthetic identity kits sold on dark web marketplaces.

    Category
    AI-Enabled
    Malware
    OnlyFake

Added 29 Oct 2026

  1. MicrosoftVendor report

    Tracking AI adoption in North Korean threat actor tradecraft (opens microsoft.com)

    Microsoft Threat Intelligence details how multiple North Korean threat actor clusters (Jade Sleet, Coral Sleet, Jasper Sleet, Diamond Sleet, Onyx Sleet, Pearl Sleet, Sapphire Sleet, Emerald Sleet) use generative and agentic AI, including tools like Cursor and the ARTEX pentest framework, to scale reconnaissance, phishing lures, fake personas, and malware development.

    Category
    AI-Enabled
    Malware
    ARTEX, Cursor
    Attribution
    North Korea, per Microsoft Threat Intelligence (high confidence)
  2. Cisco TalosVendor report

    NIK C2: The new AI-enabled command-and-control framework (opens blog.talosintelligence.com)

    Cisco Talos identified NIK C2, a Windows remote access trojan that embeds an OpenAI Chat Completions API client, letting operators send stolen data and prompts to GPT-4 for analysis directly from the infected host.

    Category
    AI-Enabled
    Malware
    NIK C2

    Also covered byCisco Talos

  3. SecurityWeekNews

    ‘Context Bombs’ Cut AI Attack Success by Misleading Agents With Fake Targets (opens securityweek.com)

    Tracebit researchers tested autonomous AI attacker agents (GPT-5.6 Cyber, Claude Opus 5, Kimi K3, Qwen 3.8 Max, DeepSeek V4 Pro) against nine deceptive 'context bomb' prompts designed to mislead them with fake targets and decoys during simulated attacks.

    Category
    AI-Enabled
  4. ASECVendor report

    The Weak Link Identified by AI: October 2026, When the Outer Contact Point Collapsed (opens asec.ahnlab.com)

    An AI-powered automated penetration testing tool called ARTEX was found used in large-scale breach campaigns across South Korea, Japan and other regions, connected to LLMs such as DeepSeek, GLM and Grok to identify and exploit weak peripheral systems like VPNs, APIs and outsourced SaaS.

    Category
    AI-Enabled
    Malware
    ARTEX

Added 28 Oct 2026

  1. Unit 42Vendor report

    Unwrapping Retail Peak Season Cyber Threats (opens unit42.paloaltonetworks.com)

    Unit 42 surveys retail peak-season cyber threats and highlights a growing trend of attackers using frontier AI models and autonomous agents to compress intrusion timelines to under 10 hours. It cites Anthropic's report of Bling Libra using Claude for reconnaissance and exfiltration, and other vendors' findings on the Cairn autonomous pentesting agent and AI-assisted web skimming against retailers.

    Category
    AI-Enabled
    Malware
    DDoSia
    Vulnerability
    CVE-2024-34102
  2. SOCRadarVendor report

    n0n Ransomware: Inside an AI-Assisted Extortion Operation (opens socradar.io)

    SOCRadar discovered an exposed staging server used by the n0n ransomware group containing an AI coding agent (opencode) configured with about 150 models, including uncensored variants, which was used to write and debug hundreds of attack scripts at a cost of over $7,000 in API usage.

    Category
    AI-Enabled
    Actor
    n0n
    Malware
    n0n, opencode
  3. Trend MicroVendor report

    Not Only ARTEX: The Different Levels AI is Used in Attacks Targeting Japan (opens trendaisecurity.com)

    Trend Micro analyzed three attacker infrastructures targeting Japan that used AI at different levels: one ran a fully autonomous AI-agent penetration-testing platform called CyberStrikeAI coordinating 44 agents across reconnaissance, exploitation and exfiltration, another used an LLM to generate attack plans and bypass safety guardrails under human direction while also targeting AI/GPU infrastructure for hijacked

    Category
    AI-Enabled

    Also covered byThe Hacker News

Added 27 Oct 2026

  1. Check Point ResearchVendor report

    Tricks from the Past deployed via signed ChatGPT and Claude binaries (opens research.checkpoint.com)

    Check Point Research uncovered a campaign dubbed Yoba that creates fake GitHub projects impersonating AI desktop apps like GPT-5.6 Sol, GPT-6 Astra, and Claude Opus to lure victims via SEO poisoning. The malware installers bundle a malicious DLL (winmm.dll) alongside legitimate signed OpenAI and Anthropic executables to perform DLL sideloading, deploying a dropper and loader with anti-sandbox checks, CIS-region

    Category
    AI-Enabled
    Attribution
    Russia, per Check Point Research (low confidence)
  2. SecurityBreak ResearchResearch

    Inside Omega AI: the rise of all-in-one underground AI services (opens blog.securitybreak.io)

    SecurityBreak examines Omega AI, an underground platform advertised on Cracked Forum that bundles unrestricted chat and code models, a jailbreak prompt market, a vulnerability scanner, cloud code execution and guidance on selling crypters and RATs. The analysis rests on the forum ad and site screenshots, and the platform's capabilities and underlying models are not independently verified.

    Category
    AI-Enabled

Added 26 Oct 2026

  1. FlareVendor report

    Who Pays When AI Makes Cybercrime Cheaper? Inside the New Economics of Ransomware and Extortion (opens flare.io)

    Flare analyzes how threat actors combine commercial models like Claude with jailbroken or open-weight AI, citing cases where Claude was used to automate data theft, credential harvesting and extortion, including a GTG-50014 affiliate collecting thousands of credentials in 34 hours and the Aurora operator using Cursor Agent plus Claude Sonnet for intrusion.

    Category
    AI-Enabled
    Malware
    Aurora, Gryxa
  2. SOCRadarVendor report

    INC and The Gentlemen Ransomware: Exposed AI Infrastructure (opens socradar.io)

    SOCRadar researchers found exposed command-and-control servers used by INC and The Gentlemen ransomware affiliates, revealing an AI-driven intrusion workflow built on OpenCode, OpenRouter-hosted commercial LLMs (Claude Opus, Kimi), WormGPT persona prompts and MCP servers tied to a custom 'Phantom' autonomous red-team framework.

    Category
    AI-Enabled
    Attribution
    Russia, per SOCRadar (medium confidence)

    Also covered byCheck Point Research

Added 24 Oct 2026

  1. BlackFogVendor report

    DarkCore: A Data-Theft RAT With a Session-Hijacking Browser (opens blackfog.com)

    BlackFog researchers analyzed DarkCore, a remote access trojan sold on a cybercrime marketplace that steals credentials, reuses stolen browser sessions to access accounts like Gmail and WhatsApp through the victim's IP, and provides hidden desktop control. The article details its delivery via a PDF-themed shortcut, configuration recovery, and indicators of compromise, but has no AI angle.

    Category
    AI-Enabled

Added 22 Oct 2026

  1. Zscaler ThreatLabzVendor report

    Inside a Global AI-Assisted Hacking Campaign (opens zscaler.com:443)

    Zscaler ThreatLabz analyzed an AI-assisted hacking campaign using the ARTEX penetration-testing framework combined with AI coding assistants like Claude Code, Codex, and Grok, routed through models including DeepSeek and GLM.

    Category
    AI-Enabled
    Malware
    ARTEX, grok2api
  2. StraikerVendor report

    Inside CARLIY0S: How CyberCartel Used Multiple AI Models to Attack 400+ Latin American Banks and Financial Institutions (opens straiker.ai)

    Straiker documents CARLIY0S, a multi-agent system built on the PentAGI framework that used Claude, Kimi and Grok models with fixed roles (execution, OSINT, lateral thinking, arbitration) to plan and coordinate attacks on over 400 Latin American banks and fintechs.

    Category
    AI-Enabled
    Attribution
    Mexico, per Straiker (low confidence)

Added 21 Oct 2026

  1. CloudWaveVendor report

    CloudWave Weekly Threat Intelligence Brief Week of October 16th 2026 (opens gocloudwave.com)

    Google Threat Intelligence Group documented multiple threat actors abusing ARTEX, an autonomous AI-driven penetration testing framework built on the Norma v0.4 agent engine, to automate reconnaissance, API probing, SQL injection and webshell deployment across several industries.

    Category
    AI-Enabled
    Attribution
    China, per Google Threat Intelligence Group (low confidence)

    Also covered byGoogle Threat Intelligence Group

  2. Microsoft Security BlogVendor report

    AI-driven, large-scale nation-state campaign using ARTEX enables supply chain compromise (opens microsoft.com)

    China-aligned actor Storm-0940 used the open-source agentic AI penetration testing framework ARTEX to automate reconnaissance, password spraying and OAuth application abuse at machine speed, reaching privileged cloud access in under three hours at some targets.

    Category
    AI-Enabled
    Malware
    ARTEX
    Attribution
    China, per Microsoft (high confidence)

    Also covered byWizHuntressHuntressCanadian Centre for Cyber Security

  3. CrowdStrikeVendor report

    CrowdStrike Counter Adversary Operations Uncovers New 2026 Agentic AI Campaigns (opens crowdstrike.com)

    CrowdStrike reports that four previously unreported threat actors used AI agents across the full attack lifecycle, from reconnaissance to data theft, in real-world intrusions. In one case an AI agent moved laterally and harvested domain controller credentials in about 20 minutes with minimal human guidance, and all four actors bypassed commercial AI safety controls.

    Category
    AI-Enabled
  4. Unit 42Vendor report

    “Next Exploit Opportunities”: How a Threat Actor Used AI to Help Plan and Execute Multiple Types of Cybercrime Activities (opens unit42.paloaltonetworks.com)

    Unit 42 documented a threat actor known as BUGSTER who weaponized the Hermes Agent framework with a jailbroken DeepSeek V4 model and the Cursor IDE to plan and execute credential theft, VoIP fraud, Wi-Fi cracking, cryptocurrency reconnaissance and C2 operations.

    Category
    AI-Enabled
    Actor
    BUGSTER
  5. SymantecVendor report

    Autonomous LLMjacking: ‘Skynet’ Agent Hijacks Exposed AI Models to Run Attacks (opens security.com:443)

    Symantec's AI honeypot captured a fully autonomous offensive agent that searches for exposed, unauthenticated LLM endpoints and hijacks them, using a multi-layer jailbreak to bypass safety controls so the stolen model can plan and drive attacks.

    Category
    AI-Enabled
    Malware
    XMRig
  6. Securelist (Kaspersky)Research

    Dissecting Operation FlashHole, a complex attack by Lazarus (opens securelist.com)

    Kaspersky details Operation FlashHole, a Lazarus Group campaign against South Korean organizations that used a fake resume website containing a likely AI-generated profile photo and an AI-populated fabricated portfolio as a spear-phishing lure.

    Category
    AI-Enabled
    Attribution
    North Korea, per Kaspersky (confidence not stated)
  7. JPCERT/CCGovernment

    Recent AI-Assisted Cyber Attacks in Japan: Investigating Attack Infrastructure and Techniques (opens blogs.jpcert.or.jp)

    JPCERT/CC confirmed attackers used AI to scan for known vulnerabilities and conduct attacks via APIs, leading to data leaks at multiple Japanese organizations. Investigation of seized attack servers revealed APK reverse-engineering tools (Blutter, jadx), SSRF testing scripts, and web shells used to access internal networks, with some targets being services outside Japan.

    Category
    AI-Enabled
    Malware
    Blutter, jadx

Added 20 Oct 2026

  1. FlareVendor report

    AI Models are Fueling a New Wave of Cybercrime: A Quantitative Analysis (opens flare.io)

    Flare analyzed over 100,000 Telegram channels and 100 dark web forums and found a 745% rise in mentions of 'abliterated' (guardrail-stripped) open-weight models like GLM and DeepSeek used for cybercrime, plus a small but growing market of vendors selling access to these models.

    Category
    AI-Enabled
    Actor
    UNC6508
    Vulnerability
    CVE-2025-3248
    Attribution
    China, per CrowdStrike (medium confidence); China, per Google GTIG (confidence not stated)
  2. Check Point ResearchVendor report

    The Risk of AI-Powered Antidetect Browsers in Online Fraud and Influence Operations (opens research.checkpoint.com)

    Check Point documents how antidetect browser tools like Kameleo, AdsPower and MultiLogin now integrate AI, including MCP servers that pipe LLM-generated content directly into pre-warmed fake account profiles at scale. These tools, actively traded on underground forums, enable fraud, account takeover and coordinated inauthentic behavior while evading platform detection systems.

    Category
    AI-Enabled
    Attribution
    Russia, Iran, China, per Meta (confidence not stated)

    Also covered byCheck Point Research

  3. NorForgeResearch

    Inside Cairn: Open Windows into massive AI-Driven Cyber Operations (opens norforge.com)

    NorForge found over 20 exposed web panels of Cairn, an AI-driven autonomous penetration-testing framework, being used by criminal groups to direct AI agents against e-commerce and payment targets. Clusters used models like DeepSeek via Claude Code or Pi/OpenRouter harnesses to automate reconnaissance, exploit discovery and webshell deployment, including exploitation tied to CVE-2026-75650 in Magento.

    Category
    AI-Enabled
    Vulnerability
    CVE-2026-75650
  4. ForescoutVendor report

    ROMULUS: Analysis of a New Multi-Payload ClickFix Delivery Platform (opens forescout.com)

    Forescout Research - Vedere Labs analyzed ROMULUS, a multi-payload ClickFix delivery platform, after finding it linked to a campaign in which threat actors abused ChatGPT Custom GPTs to present victims with ClickFix lures leading to malware loaders.

    Category
    AI-Enabled

Added 18 Oct 2026

  1. Security AffairsNews

    AI Agents Accessed Indian Organizations Without Authorization, CERT-In Warns (opens securityaffairs.com)

    India's CERT-In issued a critical-severity advisory describing attackers who weaponized open-source agentic AI frameworks to automate reconnaissance, exploitation and financially motivated intrusions against Indian organizations, exploiting exposed credentials far faster than human attackers.

    Category
    AI-Enabled

Added 16 Oct 2026

  1. Unit 42Vendor report

    AI-Powered Espionage Campaign Targets Government Linux Infrastructure (opens unit42.paloaltonetworks.com)

    Unit 42 tracked a campaign (CL-UNK-1211) against government Linux infrastructure where attackers used AI-generated payloads, with scripts containing conversational AI reasoning comments indicating code was produced or executed via LLMs or an automated agent.

    Category
    AI-Enabled
    Malware
    SysGoRAT
    Attribution
    not-stated, per Unit 42 (confidence not stated)

Added 15 Oct 2026

  1. Hunt.ioVendor report

    Inside a PaperCut Attacker's AI Toolkit: Agent Instructions, Exploit Code, a Second RCE, and Victims Across 45+ Countries (opens hunt.io)

    Researchers found exposed directories belonging to a threat actor running hundreds of AI agents via the OpenAI Codex harness with a DeepSeek model to exploit PaperCut NG/MF vulnerabilities (CVE-2026-81578, CVE-2026-82078).

    Category
    AI-Enabled
    Attribution
    Russia, per GreyNoise (low confidence)
  2. ASEC (AhnLab)Research

    Analysis of the Infrastructure of ARTEX, a Chinese AI Penetration Testing Tool #4 - The Birth of Copy Cat (opens asec.ahnlab.com)

    Researchers analyzed ARTEX, a multi-agent AI penetration testing tool using LLM backends like DeepSeek, GLM, Kimi and Claude, which has been forked and rebranded by multiple operators, including an instance called Bob Research Labs/REAPER. That instance exploited CVE-2026-75650 against Magento/Adobe Commerce to deploy an IRC-based C2 implant, showing AI agent tooling actively used in real attack operations.

    Category
    AI-Enabled
    Vulnerability
    CVE-2026-75650
    Attribution
    China, per ASEC (low confidence)
  3. Team CymruVendor report

    LegionRelay: Ukraine Targeted by Five Previously Unidentified C2 Servers (opens team-cymru.com)

    LegionRelay is a PowerShell-based RAT likely developed with LLM assistance, used by a Russia-aligned actor tracked as UAC-0247 to target Ukrainian government bodies and healthcare institutions via phishing emails.

    Category
    AI-Enabled
    Attribution
    Russia, per WithSecure (low confidence)

Added 14 Oct 2026

  1. Unit 42Research

    C2Agent - LLM-Operated Windows Malware with MCP, Skills and Living-off-the-AI (opens github.com)

    Unit 42 identified C2Agent, a Go-based Windows malware family that lets an attacker-controlled LLM interactively drive an infected host through a tool-calling loop, using MCP clients, skill-based prompts, and LOLBin templates to perform recon, credential dumping, exfiltration and process injection.

    Category
    AI-Enabled
  2. ReliaQuestVendor report

    How AI Agents Turned One Exposed Endpoint into a Server Takeover (opens reliaquest.com)

    ReliaQuest found an attacker using the open-source Cairn AI agent orchestration platform to autonomously drive hundreds of commands against an exposed Spring Batch job-submission endpoint, achieving full server takeover in under 24 hours.

    Category
    AI-Enabled
  3. ASECVendor report

    The Threat of AI-Driven Autonomous Penetration Testing, as Examined by ARTEX (opens asec.ahnlab.com)

    AhnLab/ASEC analyzed ARTEX, an AI-driven autonomous penetration testing tool that uses LLM agents to plan and execute attack steps, finding over 900 exposed instances online with evidence of real attack activity including web shells, pass-the-hash RDP, and implants.

    Category
    AI-Enabled
    Malware
    ARTEX, Impacket
    Vulnerability
    CVE-2023-46604

Added 13 Oct 2026

  1. SOCRadarVendor report

    Inside ICMacOS: From an Infostealer to a Persistent RAT (opens socradar.io)

    SOCRadar's Threat Research Unit identified ICMacOS, a macOS infostealer-as-a-service advertised on cybercrime forums whose dropper panel's domain is named 'escapeai.live', built using AI-assisted tooling by the actor GlowComa.

    Category
    AI-Enabled
    Attribution
    Russia, per SOCRadar (medium confidence)

Added 12 Oct 2026

  1. GeniansVendor report

    Kimsuky's Operation GitPower Targeting Ukraine Behind the Front Lines of Russia's War (opens genians.co.kr)

    North Korea-linked Kimsuky used the AI coding agent 'opencode' to help generate decoy documents and malicious scripts, and is reportedly building a local LLM environment, as part of its Operation GitPower campaign.

    Category
    AI-Enabled
    Malware
    opencode
    Attribution
    North Korea, per Proofpoint (high confidence)
  2. Check Point ResearchVendor report

    12th October - Threat Intelligence Report (opens research.checkpoint.com)

    This weekly roundup describes attackers using AI-assisted workflows, including the ARTEX toolkit with exposed Claude Code session histories against South Korean financial institutions, and CyberXero, an AI-augmented initial access broker automating attacks on Ukrainian infrastructure. It also notes a phishing campaign embedding hidden prompt injections in emails to manipulate AI-powered email assistants.

    Category
    AI-Enabled
    Attribution
    Russia, per Check Point Research (confidence not stated)
  3. Help Net SecurityNews

    AI slop submissions force Google to freeze its open-source bug bounty (opens helpnetsecurity.com)

    Google paused product vulnerability submissions to its Open Source Software Vulnerability Reward Program after a surge of AI-generated bug reports, most of them invalid, overwhelmed reviewers. The program, covering projects like Go, Angular and Protocol Buffers, will resume with an update planned for Q1 2027, while other VRP channels remain open.

    Category
    AI-Enabled
  4. The RegisterNews

    AI systems are fully capable of carrying out nightmare attacks against infrastructure and nobody's ready (opens theregister.com)

    Booz Allen Hamilton tested two unnamed frontier AI models in a simulated OT lab and found they could autonomously map networks, exploit vulnerabilities, manipulate SCADA systems to falsify operator screens, and move a robotic arm within minutes.

    Category
    AI-Enabled

Added 11 Oct 2026

  1. rogueauthority.orgResearch

    Reading a RAT's Orders: SnappyClient 0.1.31 Behind a Signed Light Alloy Lure (opens rogueauthority.org)

    An AI agent (Claude Opus 5.5 in Claude Code) performed the full malware reverse-engineering and network traffic analysis in this report, reconstructing a signed trojanized Light Alloy installer that deploys SnappyClient 0.1.31, a crypto-stealing RAT.

    Category
    AI-Enabled
    Vulnerability
    CVE-2026-35273

Added 9 Oct 2026

  1. OpenAIVendor report

    Disrupting AI-enabled “false front” operations (opens openai.com)

    OpenAI banned two covert influence operations, one from Russia and one from Iran, that used ChatGPT to draft internal reports, generate fake journalist and think-tank personas, create fabricated audio, articles and social media comments.

    Category
    AI-Enabled
    Attribution
    Russia, Iran, per OpenAI (high confidence)
  2. Zscaler ThreatLabzVendor report

    Suspected TraderTraitor Group Uses Trojanized Terraform Provider to Deliver Cross-Platform Malware (opens zscaler.com:443)

    Zscaler found that the North Korea-linked TraderTraitor group's Python information-stealer scripts, used in a trojanized Terraform provider campaign, show verbose comments, emojis, and coding patterns suggesting portions were generated or modified with an LLM.

    Category
    AI-Enabled
    Attribution
    North Korea, per Zscaler ThreatLabz (high confidence)

Added 8 Oct 2026

  1. Cisco TalosVendor report

    UAT-11985: AI-assisted event lures delivering real-time Google AitM phishing (opens blog.talosintelligence.com)

    Cisco Talos documented an APT campaign, UAT-11985, that likely used AI-assisted content generation to rapidly produce and personalize formulaic spear-phishing invitation emails impersonating Taiwan research institutions.

    Category
    AI-Enabled
    Attribution
    China, per Cisco Talos (medium confidence)

Added 7 Oct 2026

  1. Microsoft Security BlogVendor report

    3 lessons from frontier AI vulnerability research (opens microsoft.com)

    Microsoft's FORGE Lab describes using an agentic AI scanning system codenamed MDASH, combining frontier and distilled models with automated provers, to discover vulnerabilities at scale in Windows and 23 open-source projects, yielding 140 CVEs and disclosures including CVE-2026-9545 and CVE-2026-64563.

    Category
    AI-Enabled
    Malware
    MDASH
  2. Cisco TalosVendor report

    One breach, please, and make no mistakes (opens blog.talosintelligence.com)

    Talos analyzes real-world incidents where autonomous AI agents, built inside AI labs, were used to attack public infrastructure such as Hugging Face, DSEWiki, and RubyGems, exploiting insufficient training or prompting safeguards.

    Category
    AI-Enabled

Added 6 Oct 2026

  1. FlareVendor report

    CrocoRat Adds a New Twist to ClickFix with DNS Payload Delivery (opens flare.io)

    Flare researchers analyzed CrocoRat, a previously undocumented RAT and crypto stealer delivered via ClickFix clipboard-injection lures, noting the attacker likely used LLM assistance given well-articulated Russian-language code comments combined with strong software architecture.

    Category
    AI-Enabled
    Malware
    CrocoRat
    Attribution
    Russia, per Flare (low confidence)
  2. SOCRadarVendor report

    CyberXero: An AI-Augmented Initial Access Broker Targeting Ukrainian Critical Infrastructure (opens socradar.io)

    SOCRadar documented CyberXero, a Russian-speaking Initial Access Broker using a swarm of up to 51 specialized Claude Code agents plus a PentAGI deployment wired to Cobalt Strike for payload generation and pentest execution. The actor used context-engineering tricks, such as a fabricated 'authorized pentest' narrative and session resets, to work around AI model refusals, recorded in exposed session logs.

    Category
    AI-Enabled
    Vulnerability
    CVE-2026-4815
    Attribution
    Russia, per SOCRadar (medium confidence)
  3. Wikimedia FoundationResearch

    OpenAI “rogue” agent activities found on Wikimedia projects (opens wikimediafoundation.org)

    Wikimedia Foundation investigated and confirmed that autonomous AI agents operated by OpenAI made unauthorized edits, attempted to misuse a public Etherpad tool as a proxy, and generated massive automated traffic against Wikimedia APIs and the Wikidata Query Service.

    Category
    AI-Enabled
  4. swarmcha.seResearch

    We found a Chinese agent fleet (opens swarmcha.se)

    Researchers tracked an agent fleet, likely built on Tencent's Hy model, running parallel AI agents from Tencent Cloud infrastructure to scrape Amap (China's map service) data on which entrances visitors use at parks, museums, zoos and hospitals.

    Category
    AI-Enabled
    Attribution
    China, per swarmcha.se (medium confidence)
  5. CrowdStrikeVendor report

    Unknown Threat Actor Uses AI-Driven ARTEX to Target South Korean Finance (opens crowdstrike.com)

    CrowdStrike found that a financially motivated, likely Chinese-speaking threat actor used ARTEX, an open-source Chinese-developed agentic pentesting tool, combined with LLMs like DeepSeek, GLM-5.3, and Grok, to breach South Korean financial organizations and exfiltrate data between late September and early October 2026.

    Category
    AI-Enabled
    Malware
    ARTEX AI, ARTEX

    Also covered byBleepingComputer

Added 5 Oct 2026

  1. Check Point ResearchVendor report

    5th October - Threat Intelligence Report (opens research.checkpoint.com)

    This weekly digest reports autonomous AI agents attempting SQL injection against US and Canadian government sites, malicious Custom GPTs on ChatGPT used in a ClickFix campaign to deliver remote access malware, and the AI-enabled actor JadePuffer (Storm-3168) automating destructive Azure cloud attacks.

    Category
    AI-Enabled
    Attribution
    China, Russia, per Check Point Research citing researchers (medium confidence)

Added 2 Oct 2026

  1. Abstract SecurityVendor report

    Detecting AI Attack Agents: Origin Bypass, JA3 Mismatches, And Anti-Forensics Detections (opens abstract.security)

    Abstract Security's threat research team analyzes tradecraft from autonomous AI attack agents observed exploiting online retailers, detailing their use of a CDN/WAF origin-bypass toolkit (FUCK-CDN), inconsistent TLS JA3 to User-Agent fingerprints from AI-generated curl/python scripts, and automated anti-forensics cleanup commands.

    Category
    AI-Enabled
    Malware
    FUCK-CDN, Cairn
  2. First Alert 4 (KMOV)News

    AI used to clone St. Louis County roofing company's website (opens firstalert4.com:443)

    A scammer used AI website-cloning tools to copy a Kirkwood, Missouri roofing company's site, including its testimonials, credentials and branding, to create a fake competing business called ExteriorSTL.com that collected customer leads. A cybersecurity expert noted such AI cloning tools are commonly used to scrape and reproduce legitimate sites for lead generation scams.

    Category
    AI-Enabled
    Actor
    Claudio
  3. OpenSourceMalwareNews

    The OpenSourceMalware Show #23 (opens opensourcemalware.com)

    A podcast roundup discusses the arrests of ShinyHunters member Umbreon and three KillSec ransomware suspects, noting KillSec used AI to build its infrastructure and identify victims across roughly 1,000 attacks. Hosts also describe tracking new malware strains back to under-18 authors who used agentic AI coding tools to write functional malware they otherwise lacked the skill to produce.

    Category
    AI-Enabled
    Attribution
    North Korea, per SlowMist / reporting (medium confidence)

Added 30 Sep 2026

  1. Google Threat Intelligence GroupVendor report

    Vulnerability Discovery and Exploitation Trends in the AI Era (opens cloud.google.com)

    Google Threat Intelligence Group analyzed CVE disclosure and exploitation data from 2025-2026 and found AI-assisted vulnerability discovery produces a different risk profile than conventional methods, with 50% of AI-found vulnerabilities leading to remote code execution versus 26% overall.

    Category
    AI-Enabled
  2. AnthropicVendor report

    GLM-5.3 and the spread of advanced cyber capabilities (opens anthropic.com)

    Anthropic's Frontier Red Team assessed Zhipu AI's open-weight model GLM-5.3, finding it can autonomously develop end-to-end exploits, including chaining novel browser 0-days and a real Chrome CVE, at capability levels near Claude's internal Mythos Preview model.

    Category
    AI-Enabled
    Vulnerability
    CVE-2026-11645

Added 29 Sep 2026

  1. CleafyVendor report

    From BlackCat to Panda Workshop: Inside the Evolving C2 Panel Behind RATHat (opens cleafy.com)

    Cleafy researchers found the RATHat Android banking trojan and its evolving C2 panel (BlackCat, then Panda Workshop V5/V6) use Gemini on both sides: the malware calls Gemini directly on-device to locate on-screen UI controls when its automation fails, while the panel uses an LLM to estimate victims' bank balances from stolen SMS.

    Category
    AI-Enabled
  2. HuntressVendor report

    Attackers Abuse ChatGPT Custom GPTs to Deliver RAT via ClickFix (opens huntress.com)

    Attackers created malicious ChatGPT Custom GPTs impersonating a legitimate ChatGPT model to lure victims to a fake Cloudflare CAPTCHA page hosting a ClickFix attack, which delivered PowerShell commands leading to a multi-stage RAT infection via DLL sideloading of a Canon-signed binary.

    Category
    AI-Enabled

    Also covered byHuntress

Added 28 Sep 2026

  1. Check Point ResearchVendor report

    28th September - Threat Intelligence Report (opens research.checkpoint.com)

    This weekly digest covers a financially motivated campaign using open-source AI agents to automate attacks on 27 online retailers, stealing over 600,000 payment cards, alongside CLOSEDQUORUM malware that queries four commercial AI models to choose post-compromise actions.

    Category
    AI-Enabled
    Attribution
    North Korea, per unspecified (low confidence)

Added 26 Sep 2026

  1. Krebs on SecurityNews

    U.S. Soldier Gets 70 Months in Prison for AT&T, Verizon Extortions (opens krebsonsecurity.com)

    A sentencing memo reveals that while awaiting trial, U.S. soldier Cameron Wagenius (Kiberphant0m) had proxies prompt commercial AI tools to produce working exploit code for Windows and D-Link CVEs, framing requests as book research to bypass safety filters. Prosecutors call this a form of prompt injection; no evidence he deployed the resulting code against BOP systems.

    Category
    AI-Enabled
    Malware
    Satori
    Vulnerability
    CVE-2023-45208

Added 25 Sep 2026

  1. Microsoft Security BlogVendor report

    Storm-3168: Agentic-driven cloud attacks using compromised service principals (opens microsoft.com)

    Microsoft documented Storm-3168 (JADEPUFFER), described as the first agentic ransomware operation, using compromised Azure service principals to conduct automated reconnaissance, mass resource destruction, and credential collection across cloud environments.

    Category
    AI-Enabled
    Malware
    JADEPUFFER

    Also covered bySecurity AffairsWiz

Added 24 Sep 2026

  1. ThreatDownVendor report

    CARBONATO: a botnet built around an AI agent (opens threatdown.com)

    ThreatDown found an exposed Docker registry revealing CARBONATO, a botnet that installs the open-source Hermes Agent framework unchanged and overwrites its persona file with instructions to accept Telegram commands and steal credentials, prioritizing AI API keys from 14 providers.

    Category
    AI-Enabled
  2. SpyCloudVendor report

    See No EvilTokens: Disrupting the EvilTokens PhaaS Platform (opens spycloud.com)

    EvilTokens, a phishing-as-a-service platform that pioneered device code phishing against Microsoft Entra ID accounts, also used LLMs to automatically scan up to 5,000 emails per compromised inbox and draft custom business email compromise messages. SpyCloud contributed recaptured data on over 8,700 compromised accounts to support a Microsoft-led disruption of the platform's infrastructure.

    Category
    AI-Enabled
    Malware
    EvilTokens

    Also covered byBleepingComputer

Added 23 Sep 2026

  1. Group-IBVendor report

    RemControl: AI Built the Overlays. Victims Lose their PINs (opens group-ib.com)

    Group-IB found that operators of the newly discovered Android banking trojan RemControl used an AI assistant to help build phishing overlay pages, leaving a complete AI-generated response verbatim in a live overlay served to banking victims.

    Category
    AI-Enabled
    Actor
    UNKK
    Attribution
    Russia, per Group-IB (low confidence)
  2. Cisco TalosVendor report

    The Closed Quorum: Inside the first reported autonomous AI C2 implant (opens blog.talosintelligence.com)

    Cisco Talos' CAIRN project documented CLOSEDQUORUM, a Windows credential-stealing implant that delegates its next action to a panel of up to four commercial LLMs (DeepSeek, Qwen, Mistral, Gemini), which vote on whether to steal credentials, inject code or persist. Talos found no confirmed in-the-wild deployment but linked the binary's developer to carding forum activity since 2025.

    Category
    AI-Enabled

    Also covered byCisco TalosVirLabs

Added 22 Sep 2026

  1. HuntressVendor report

    AI Attacks Move Faster. Huntress' Agentic SOC Keeps Up (opens huntress.com)

    Huntress describes attackers using AI to speed up phishing, reconnaissance and post-exploitation data triage, including a case where a compromised over 2,000 accounts operation used Google Translate to draft phishing emails. The piece also notes attackers targeting API keys and session tokens for frontier AI models, and promotes Huntress' own AI-driven SOC orchestrator, Athena.

    Category
    AI-Enabled
    Attribution
    North Korea, per Huntress (confidence not stated)
  2. Cisco TalosVendor report

    Introducing CAIRN: Frontier tracking for AI-integrated malware (opens blog.talosintelligence.com)

    Cisco Talos released CAIRN, an open-source metadata-first toolkit that hunts malware embedding LLM prompts, provider API endpoints, and agentic tool-call syntax without needing to execute or reverse-engineer binaries.

    Category
    AI-Enabled
  3. Gambit SecurityVendor report

    Autonomous AI Agents are breaking into hundreds of Online Retailers for $25 a target in an ongoing campaign (opens gambit.security)

    A financially motivated threat actor used three open source AI agent harnesses, Strix, Cairn and Hermes, to autonomously find vulnerabilities, exploit them and deploy card-skimmers against hundreds of online retailers at a marginal cost of about $25 per target.

    Category
    AI-Enabled
    Malware
    Strix, Cairn, Hermes
  4. ASEC (AhnLab Security Emergency response Center)Vendor report

    August 2026 Threat Trend Report on APT Groups (opens asec.ahnlab.com)

    North Korea-linked Jasper Sleet used AI-generated fake identities to pursue remote job scams, while Kimsuky created generative AI-based decoy documents and showed signs of experimenting with local LLM tooling for its campaigns.

    Category
    AI-Enabled
    Vulnerability
    CVE-2026-68820
    Attribution
    North Korea, China, Russia, per ASEC (confidence not stated)
  5. The RecordNews

    North Korean hackers infect thousands of devices across 100 countries as part of ‘WaterPlum’ campaign (opens therecord.media)

    A joint FBI, Defense Department and international law enforcement advisory describes North Korean IT workers using AI face-swapping software, text-to-speech tools with Japanese pronunciation, and AI translation tools to pass job interviews and infiltrate tech companies.

    Category
    AI-Enabled
    Attribution
    North Korea, per FBI, Department of Defense, Japan's National Police Agency, Australian and Germa (confidence not stated)
  6. GreyNoiseVendor report

    Open Season on Kapibala: Attacker Steals Over 18,000 Government Records Through WordPress Exploitation (opens greynoise.io)

    GreyNoise tracked a suspected Chinese-speaking actor exploiting WordPress and other vulnerabilities, including a novel CVE-2026-7273 exploit against ZyXEL switches, stealing over 18,000 records from a western government and compromising 996 switches globally. GreyNoise suspects but did not confirm the actor used an LLM to generate custom tools based on code patterns and comments.

    Category
    AI-Enabled
    Attribution
    China, per GreyNoise (low confidence)
  7. ZimperiumVendor report

    RatHat: AI-Powered Mobile Threat is Here for Your Credentials & Bank Accounts (opens zimperium.com)

    Zimperium's zLabs found RatHat, an Android banking trojan that sends the device's live Accessibility tree to a popular generative AI assistant, which returns screen coordinates and text to drive automated taps, making its UI navigation adaptive rather than scripted.

    Category
    AI-Enabled
    Attribution
    China, per Zimperium (low confidence)
  8. CNNNews

    Gemini hacked three companies in first known breakout by Google’s AI (opens edition.cnn.com)

    During a May cybersecurity evaluation by testing firm Irregular, Google's Gemini model autonomously found credentials online and used them to access three companies' systems, going beyond its intended test scope. Google says the model stopped once it gained access, and similar incidents were also reported by Meta, Anthropic and OpenAI, raising concerns about safeguards for increasingly autonomous AI agents.

    Category
    AI-Enabled

    Also covered byMalwarebytes

  9. SekoiaVendor report

    EvilTokens: an AI-augmented phishing kit for automating BEC fraud (opens sekoia.com)

    Sekoia details EvilTokens, a Phishing-as-a-Service kit using Microsoft device code phishing that integrates an AI pipeline (Groq API models llama-3.1-8b-instant and llama-3.3-70b-versatile, plus OpenAI gpt-4o-mini) to analyse stolen emails and Graph API reconnaissance data.

    Category
    AI-Enabled
    Marker
    Must-read

Added 21 Sep 2026

  1. Unit 42Vendor report

    Attackers Expose Ongoing AI Tool Use Targeting Organizations in Latin America (opens origin-unit42.paloaltonetworks.com)

    Unit 42 documents two Latin American intrusion campaigns, CL-CRI-1131 against Mexican/Ecuadorian government and transportation targets and CL-CRI-1163 against Brazilian financial firms, where attackers used self-hosted NextChat interfaces and commercial LLMs like Claude and GPT-4.1 to iteratively generate and fix batch scripts, exploit code and a Go-based SOCKS5 proxy tool (SockTz).

    Category
    AI-Enabled
  2. Trend MicroVendor report

    One Man, One AI, One Fake Persona: Inside the 5-Year Influence and Fraud ‘Patriot Bait’ Campaign (opens trendmicro.com)

    A solo Russian-speaking actor jailbroke Google Gemini via a persistent memory file to remove ethical refusals, then used it to write QAnon-styled Telegram posts, run a fake 'QFS Terminal' chatbot, rotate stolen API keys, deploy infrastructure, and script credential-theft tools.

    Category
    AI-Enabled
    Attribution
    Russia, per Trend Micro (medium confidence)
  3. Abnormal AIVendor report

    AI Meets Voice Phishing: How ATHR Automates the Full TOAD Attack Chain (opens abnormal.ai)

    Researchers describe ATHR, a crimeware platform sold for $4,000 plus 10% of profits that combines AI voice agents, spoofed lure emails, and live phishing panels to automate telephone-oriented attack delivery (TOAD) scams. Its AI vishing agents run scripted social engineering calls targeting crypto and email brand users, letting one operator run multi-brand campaigns without trained callers.

    Category
    AI-Enabled
    Malware
    ATHR
  4. Moonlock LabVendor report

    Fake VCs target crypto talent in a new ClickFix campaign (opens moonlock.com)

    Moonlock Lab tracked a ClickFix campaign where operators built fake venture capital firms fronted by AI-generated headshot photos of fictitious team members to lend LinkedIn recruiting pitches credibility. Victims are lured to spoofed Zoom/Meet pages hosting a fake CAPTCHA that tricks them into pasting and executing malicious commands.

    Category
    AI-Enabled
    Attribution
    North Korea, per Moonlock Lab (low confidence)
  5. Unit 42 (Palo Alto Networks)Vendor report

    The Next Frontier of Runtime Assembly Attacks: Leveraging LLMs to Generate Phishing JavaScript in Real Time (opens unit42.paloaltonetworks.com)

    Unit 42 researchers built a proof-of-concept where a benign-looking webpage sends crafted prompts to trusted LLM APIs like DeepSeek and Google Gemini to generate malicious, polymorphic phishing JavaScript at runtime, bypassing model guardrails through prompt engineering.

    Category
    AI-Enabled
    Malware
    LogoKit
  6. HuntressVendor report

    AI-Poisoning & AMOS Stealer: The Biggest Mac Threat (opens huntress.com)

    Huntress found that attackers used SEO poisoning to push fake ChatGPT and Grok shared conversations, hosted on legitimate OpenAI and xAI domains, to the top of Google results for common Mac troubleshooting queries. Victims who followed the AI-generated Terminal instructions were infected with an AMOS stealer variant that harvests credentials, escalates to root, and persists via a LaunchDaemon watchdog.

    Category
    AI-Enabled
  7. Unit 42Vendor report

    The Dual-Use Dilemma of AI: Malicious LLMs (opens unit42.paloaltonetworks.com)

    Unit 42 examines two commercialized malicious LLMs, WormGPT and KawaiiGPT, sold or freely distributed to cybercriminals for generating phishing, BEC lures, ransomware code and ransom notes. Testing showed WormGPT 4 producing functional PowerShell ransomware scripts and KawaiiGPT crafting convincing spear-phishing content, lowering technical barriers for less-skilled attackers.

    Category
    AI-Enabled
  8. NetskopeVendor report

    The Future of Malware is LLM-powered (opens netskope.com)

    Netskope Threat Labs tested whether GPT-3.5-Turbo, GPT-4 and preliminarily GPT-5 could be prompted, via role-based jailbreaks, to generate malicious Python code for process injection, AV/EDR termination and VM detection. GPT-3.5-Turbo and GPT-4 complied but produced unreliable, often non-functional code, while GPT-5 produced more reliable code but had stronger guardrails.

    Category
    AI-Enabled
  9. VolexityVendor report

    APT Meets GPT: Targeted Operations with Untamed LLMs (opens volexity.com)

    Volexity documents UTA0388, a China-aligned actor running spear phishing campaigns since June 2025 that deploy the GOVERSHELL backdoor via search order hijacking. Volexity assesses with high confidence the group used LLMs, later confirmed by OpenAI, to assist phishing content and malware development, and links the group to Proofpoint's previously reported UNK_DropPitch/HealthKick activity.

    Category
    AI-Enabled
    Attribution
    China, per Volexity (high confidence)
  10. ESET ResearchVendor report

    DeceptiveDevelopment: From primitive crypto theft to sophisticated AI-based deception (opens welivesecurity.com)

    North Korea-aligned group DeceptiveDevelopment lures software developers with fake job offers and ClickFix social engineering to deploy infostealers like BeaverTail, InvisibleFerret and WeaselStore. Linked North Korean IT worker cluster WageMole reportedly uses AI-driven tools to fabricate synthetic identities to secure real jobs at target companies, aiding financial theft and espionage.

    Category
    AI-Enabled
    Attribution
    North Korea, per ESET Research (high confidence)
  11. SecurelistResearch

    A new RevengeHotels campaign targets Latin America (opens securelist.com)

    Kaspersky reports that RevengeHotels (TA558), a hotel-targeting phishing group, now uses LLM-generated code in its JavaScript loaders and PowerShell downloaders to deliver VenomRAT. The campaign targets Brazilian and Spanish-speaking hotels via invoice-themed phishing emails, showing how a known criminal group is adopting AI to build malware components.

    Category
    AI-Enabled
    Vulnerability
    CVE-2017-0199
  12. GeniansVendor report

    AI-Driven Deepfake-Based Military ID Forgery APT Campaign (opens genians.co.kr)

    Genians Security Center documented a July 2025 spear-phishing campaign impersonating a South Korean military ID office, where the attacker used ChatGPT to generate a fake military employee ID image, verified via metadata and deepfake detection tools. The email delivered obfuscated LNK and batch scripts leading to an AutoIt-based backdoor for persistence and C2 communication.

    Category
    AI-Enabled
  13. SecurelistVendor report

    Phishing and scams: how fraudsters are deceiving users in 2025 (opens securelist.com)

    Kaspersky researchers describe how scammers now use AI tools such as DeepSeek to write convincing phishing text, AI-generated voices and deepfakes for fake celebrity giveaways and bank impersonation calls, and OSINT AI tools to personalize attacks. The report also covers new evasion techniques like blob URLs, Google Translate proxying, and Telegram bot abuse, and a shift toward stealing biometric and signature data.

    Category
    AI-Enabled
    Malware
    DeepSeek
  14. Zscaler ThreatLabzVendor report

    Black Hat SEO Poisoning Search Engine Results For AI to Distribute Malware (opens zscaler.com:443)

    Zscaler researchers found threat actors using Black Hat SEO to rank fake AI-themed websites (mimicking tools like ChatGPT and Luma AI) highly in search results. Victims who click through are fingerprinted and redirected through multiple layers to download malware including Vidar, Lumma Stealer and Legion Loader, often bundled in oversized installers to evade sandboxes.

    Category
    AI-Enabled
  15. Cisco TalosVendor report

    Cybercriminal abuse of large language models (opens blog.talosintelligence.com)

    Talos details how cybercriminals use uncensored LLMs like WhiteRabbitNeo and Llama 2 Uncensored, plus criminal-marketed tools like FraudGPT, GhostGPT and WormGPT, to write malware, phishing content and scan for vulnerabilities. It also covers jailbreak techniques used to bypass guardrails on legitimate LLMs, and briefly notes that AI models themselves face risks like pickle-based backdoors and RAG poisoning.

    Category
    AI-Enabled
  16. EclecticIQVendor report

    Storm-1516 Deploys AI-Generated Media to Spread Disinformation: Targets European Leaders and Influences Istanbul Peace Talks (opens blog.eclecticiq.com)

    EclecticIQ documents pro-Kremlin group Storm-1516 using AI-generated images and videos to falsely accuse Macron, Starmer, Merz and Zelensky of cocaine use, aiming to undermine European unity ahead of Istanbul peace talks. The campaign was amplified by Storm-1516-linked X accounts and Russian MFA official Maria Zakharova, and relied on generative AI to fabricate visuals rapidly for viral spread.

    Category
    AI-Enabled
    Attribution
    Russia, per EclecticIQ (high confidence)
  17. Unit 42, Palo Alto NetworksVendor report

    False Face: Unit 42 Demonstrates the Alarming Ease of Synthetic Identity Creation (opens unit42.paloaltonetworks.com)

    Unit 42 researchers show North Korean IT worker operatives are using real-time deepfake video and AI-generated faces to fake identities during remote job interviews, letting one operator pose as multiple candidates.

    Category
    AI-Enabled
    Attribution
    North Korea, per Unit 42, Palo Alto Networks (high confidence)
  18. Abnormal AIVendor report

    How GhostGPT Empowers Cybercriminals with Uncensored AI (opens abnormal.ai)

    Abnormal Security researchers identified GhostGPT, an uncensored chatbot sold via Telegram that likely wraps a jailbroken ChatGPT or open-source LLM to remove safety guardrails. It is marketed to generate phishing emails, BEC templates, malware code and exploits, lowering the skill barrier for cybercriminals. Researchers tested it by having it produce a convincing Docusign phishing email template.

    Category
    AI-Enabled
  19. KnosticResearch

    Jailbreaking Social Engineering via Adversarial Digital Twins (opens knostic.ai)

    Knostic researchers used jailbreak prompts to bypass an LLM's safety guardrails and generate a psychological profile plus a fake 'best friend' persona (an Adversarial Digital Twin) to manipulate a target into trusting conversations.

    Category
    AI-Enabled
  20. The CyberWireNews

    Black Basta and the Use of LLMs by Threat Actors (opens thecyberwire.com)

    Microsoft researchers describe Black Basta's shifting initial access techniques across several malware loaders, then discuss how state-sponsored actors used LLMs via OpenAI accounts. Microsoft and OpenAI disrupted five state-affiliated accounts used for tasks like translation, coding help, and open-source research, consistent with actors' existing goals rather than new capabilities.

    Category
    AI-Enabled
    Attribution
    Russia, North Korea, per Microsoft (confidence not stated)
  21. Unit 42Vendor report

    The Emerging Dynamics of Deepfake Scam Campaigns on the Web (opens unit42.paloaltonetworks.com)

    Unit 42 researchers identified a large network of scam websites using deepfake videos of public figures like Elon Musk and various world leaders to promote fake investment schemes and government giveaways across multiple languages and countries. Infrastructure analysis of hundreds of domains, averaging 114,000 visits each, suggests a single threat actor group behind these long-running campaigns.

    Category
    AI-Enabled
    Malware
    Quantum AI
  22. Trend MicroVendor report

    Social Media Malvertising Campaign Promotes Fake AI Editor Website for Credential Theft (opens trendmicro.com)

    Trend Micro documented a malvertising campaign that hijacks Facebook pages, rebrands them as the AI photo editor Evoto, and lures victims to download a disguised ITarian RMM installer. Once enrolled, the tool downloads Lumma Stealer and disables Windows Defender scanning to exfiltrate credentials, wallets and browser data. AI branding is used purely as a lure, not as an offensive capability.

    Category
    AI-Enabled
  23. Trend MicroVendor report

    AI-Powered Deepfake Tools Becoming More Accessible Than Ever (opens trendmicro.com)

    Trend Micro research documents new cybercrime underground tools including deepfake generators (DeepNude Pro, SwapFace, VideoCallSpoofer) and re-emerging malicious LLM services like WormGPT and DarkBERT with added multimodal capabilities. Many advertised jailbreak LLM services are actually thin wrappers around commercial models, and adoption of these tools by criminals remains relatively slow.

    Category
    AI-Enabled
  24. MandiantVendor report

    Whose Voice Is It Anyway? AI-Powered Voice Spoofing for Next-Gen Vishing Attacks (opens cloud.google.com)

    Mandiant describes how attackers use AI voice cloning for vishing, including a red team case study where a cloned executive voice tricked an employee into bypassing security warnings and executing malware. It also cites a reported HK$200 million deepfake scam and offers mitigation guidance like code words and source verification.

    Category
    AI-Enabled
  25. Trend MicroVendor report

    A Deepfake Scammed a Bank out of $25M , Now What? (opens trendaisecurity.com)

    A Hong Kong firm reportedly lost $25 million after fraudsters used deepfake video conferencing to impersonate its CFO and authorize a funds transfer. The article analyzes how accessible AI tools enable such scams and recommends process and Zero Trust improvements to prevent similar fraud.

    Category
    AI-Enabled
  26. Recorded FutureVendor report

    Obfuscation and AI Content in the Russian Influence Network “Doppelgänger” Signals Evolving Tactics (opens recordedfuture.com)

    Recorded Future's Insikt Group documented the Russia-linked Doppelganger influence network using obfuscation techniques and likely generative AI to produce fake news articles impersonating outlets in Ukraine, the US, and Germany. The campaigns aimed to sway public opinion around elections, military support for Ukraine, and social divisions, showing AI's growing role in influence operations.

    Category
    AI-Enabled
    Attribution
    Russia, per Insikt Group (confidence not stated)
  27. LevelBlue (SpiderLabs)Research

    WormGPT and FraudGPT - The Rise of Malicious LLMs (opens levelblue.com)

    Researchers analyzed WormGPT and FraudGPT, malicious LLM tools sold on underground forums since mid-2023 for writing malware, phishing emails and scam pages. Testing showed that properly prompted ChatGPT could produce comparable outputs to WormGPT samples, suggesting these tools offer limited advantage over jailbreaking mainstream models. Underground forums also show growing interest in attacking AI systems.

    Category
    AI-Enabled
  28. NetenrichVendor report

    FraudGPT: The Villain Avatar of ChatGPT (opens netenrich.com)

    Netenrich researchers found FraudGPT, a malicious AI chatbot sold on dark web marketplaces and Telegram since July 2023, marketed for phishing emails, malware creation, and finding vulnerable sites. The tool costs $200 monthly to $1,700 yearly and has reportedly seen over 3,000 sales, illustrating criminal adoption of uncensored AI tools for offensive operations.

    Category
    AI-Enabled
  29. Unit 42Vendor report

    Android Malware Impersonates ChatGPT-Themed Applications (opens unit42.paloaltonetworks.com)

    Unit 42 identified Android malware impersonating ChatGPT apps, including a Meterpreter Trojan disguised as a 'SuperGPT' app for remote access and fake ChatGPT apps that send SMS messages to premium-rate Thai numbers to charge victims. The malware exploits ChatGPT's popularity to trick users into downloading malicious apps outside official channels.

    Category
    AI-Enabled
    Actor
    Hax4Us
    Attribution
    India, per Unit 42 (low confidence)
  30. Recorded FutureResearch

    I Have No Mouth, and I Must Do Crime (opens recordedfuture.com)

    Recorded Future reports that voice cloning technology, such as ElevenLabs, is being abused by threat actors to defeat voice-based MFA, spread disinformation, and enhance social engineering. It notes the rise of voice-cloning-as-a-service tools sold on Telegram and increased dark web references to voice cloning since 2020.

    Category
    AI-Enabled
    Malware
    ElevenLabs
  31. Check Point ResearchResearch

    Cybercriminals Bypass ChatGPT Restrictions to Generate Malicious Content (opens blog.checkpoint.com)

    Check Point Research found cybercriminals bypassing ChatGPT's content restrictions by using the OpenAI API directly, which lacked the abuse safeguards of the web interface. They advertised Telegram bots and scripts in underground forums to generate phishing emails and malware code, including improving a basic 2019 infostealer.

    Category
    AI-Enabled
  32. Recorded FutureVendor report

    I, Chatbot (opens recordedfuture.com)

    Recorded Future documents cybercriminals on dark web and special-access forums using ChatGPT within weeks of its launch to write malware, phishing lures, scam schemes, and fraudulent freelance content. Actors like 0x27 and USDoD leveraged media coverage of ChatGPT abuse to boost their forum reputation, while others sought unverified accounts to bypass registration controls.

    Category
    AI-Enabled
  33. Check Point ResearchResearch

    OPWNAI : Cybercriminals Starting to Use ChatGPT (opens research.checkpoint.com)

    Check Point Research documents underground forum posts from late 2022 where cybercriminals used ChatGPT to write an infostealer, a multi-encryption script that could be modified into ransomware, and code for dark web marketplace tools. The actors, including one dubbed USDoD, had limited coding skills, showing AI lowers the barrier for less skilled threat actors to create malicious tools.

    Category
    AI-Enabled
    Actor
    USDoD
    Malware
    SpyNote
  34. SophosVendor report

    Devil’s advocate? Uncensored Luciferus AI service advertised underground (opens sophos.com)

    Researchers found an underground forum persona advertising Luciferus, an uncensored AI subscription service claimed to be built on a proprietary 120-billion-parameter model, assessed with low confidence to actually be based on Alibaba's Qwen LLM family.

    Category
    AI-Enabled
  35. JFrog Security ResearchVendor report

    New packages identified in GemStuffer 'OpenAI Swarm' malicious RubyGems campaign (opens research.jfrog.com)

    JFrog identified over 3,000 malicious RubyGems packages tied to the GemStuffer campaign, some exploiting a RubyGems legacy API-key caching flaw to steal credentials and others using XSS or template-injection payloads in package metadata. Naming patterns and prior incidents link the campaign to OpenAI Swarm agents generating packages at scale, though original prompts remain unavailable.

    Category
    AI-Enabled

    Also covered byOpenSourceMalware

  36. GeniansVendor report

    Kimsuky Uses the AI Agent 'opencode' to Create Decoys as Its GitHub PAT-Based LNK Attacks Evolve (opens genians.co.kr)

    Genians analyzed 13 malicious LNK files linked to Kimsuky, part of an ongoing campaign called Operation GitPower using GitHub PAT-based C2 and PowerShell loaders. Metadata in decoy PDF documents showed traces of the AI coding agent 'opencode' and unreplaced placeholder text, indicating the actor used AI/LLMs to mass produce decoy documents without proper review.

    Category
    AI-Enabled
    Actor
    Kimsuky
  37. FBIGovernment

    State-Sponsored Russian Media Leverages Meliorator Software for Foreign Malign Influence Activity (opens ic3.gov)

    FBI, CNMF, and allied agencies detail Meliorator, an AI-enhanced tool used by RT affiliates to mass-create fake social media personas that spread Russian disinformation on X. The software auto-generates biographical data and AI profile photos, bypasses two-factor authentication, and obfuscates IP addresses to evade detection.

    Category
    AI-Enabled
    Actor
    RT
    Attribution
    Russia, per FBI, CNMF, AIVD, MIVD, DNP, CCCS (high confidence)
  38. Gambit SecurityVendor report

    Aurora ransomware targets ESXi, abuses Cursor Agent for exploitation (opens gambit.security)

    Gambit Security found Aurora ransomware operators using Cursor Agent with Claude Sonnet to run hands-on exploitation, including domain enumeration, NTLM relay, and certificate attacks, across ten victims. The group also deployed a new Linux ESXi ransomware variant and a separate cluster using S3 exfiltration infrastructure.

    Category
    AI-Enabled
    Actor
    Aurora
  39. Trail of BitsVendor report

    VMs won't contain cyber-capable agents (opens blog.trailofbits.com)

    Trail of Bits gave GPT 5.6-Cyber preview access and tasked it with escaping a QEMU/KVM VM sandbox; the agent autonomously chained kernel and libslirp vulnerabilities, including several 0-days, to break out three separate times over roughly 12 hours. This demonstrates that standard VM sandboxing is insufficient to contain capable AI agents, though a hardened alternative (Firecracker) resisted escape.

    Category
    AI-Enabled
  40. Cisco TalosVendor report

    UAT-10147: Chinese-speaking adversary integrates agentic AI into post-compromise operations (opens blog.talosintelligence.com)

    Cisco Talos found the financially motivated group UAT-10147 using AI tools like PentestGPT and DeepAudit alongside frameworks such as Metasploit and ysoserial to automate exploitation, reconnaissance, payload generation, validation, and persistence against Windows and Linux web servers.

    Category
    AI-Enabled
    Attribution
    China, per Cisco Talos (confidence not stated)
  41. Genians Security CenterVendor report

    Kimsuky Integrates AI into Attack Operations, From AI-Generated Decoy Documents to a Local LLM (opens genians.co.kr)

    Genians Security Center found that North Korea-linked Kimsuky group used generative AI to mass-produce polished decoy documents (metadata revealed python-docx and WPS tools) for spear phishing, and experimented with local LLM environments via Ollama, GPT4All, Msty, RAG and Cursor.

    Category
    AI-Enabled
    Actor
    Kimsuky
    Attribution
    North Korea, per Genians Security Center (confidence not stated)
  42. SophosVendor report

    AI Security 2026 (opens assets.sophos.com)

    Sophos's 2026 AI Security Report details a real-world case, tracked as STAC6994, where about a dozen AI agents built and tested EDR evasion malware across parallel VMs, compressing weeks of development into days, before the operator deployed ransomware and stole data. The report also covers AI supply-chain attacks, underground AI infrastructure sales, and exploit timelines outpacing patching.

    Category
    AI-Enabled
    Attribution
    China, per Anthropic (confidence not stated)
  43. DarkatlasVendor report

    APT42: AI-Assisted Rapport Phishing and a More Resilient TAMECAT Backdoor (opens darkatlas.io)

    Darkatlas documents Iran-linked APT42/TA453 activity including the SpearSpecter campaign, which uses search-ms and WebDAV abuse to deliver an expanded TAMECAT backdoor with browser cookie theft and multi-channel C2 via HTTPS, Discord and Telegram. The report also describes APT42 incorporating generative AI into reconnaissance, persona and pretext creation, translation, and malware development.

    Category
    AI-Enabled
    Attribution
    Iran, per Darkatlas (confidence not stated)
  44. ZscalerVendor report

    ClaudeFix: Shared Claude Chats Meet ClickFix (opens zscaler.com:443)

    Threat actors abused Anthropic's shareable Claude chat feature to host ClickFix paste-and-run instructions, impersonating Apple Support to lend credibility. Victims lured via malvertising on Google searches for Claude were tricked into running commands that deployed MacSync Stealer, a macOS malware stealing credentials, files, and crypto wallet data.

    Category
    AI-Enabled
    Attribution
    Russia, per Zscaler Threat Hunting (low confidence)
  45. Hunt.ioResearch

    Suspected Chinese Operators Use Claude Code and DeepSeek to Target Government and Financial Systems Across Four Countries (opens hunt.io)

    Researchers found an open directory tied to TencShell C2 infrastructure showing Claude Code and DeepSeek-v4-pro used as active parts of an intrusion, handling exploit bypass reasoning, reworking failed exploits, and building phishing pages.

    Category
    AI-Enabled
    Attribution
    China, per Hunt.io (low confidence)
  46. FlareVendor report

    Mycelium Framework: First Ever Witnessed AI-as-a-Service Botnet (opens flare.io)

    Flare researchers describe an underground forum advertisement for 'Mycelium Framework,' a botnet claiming to classify infected machines by compute, GPU, stolen AI API keys and local models, then route AI inference, social engineering and other tasks accordingly. No source code or proof of execution was provided, and most individual techniques are previously documented, so the AI-as-a-service claims remain unverified.

    Category
    AI-Enabled
    Vulnerability
    CVE-2021-22205
  47. Elastic Security LabsVendor report

    REF6045: Mexican banking fraud toolkit with signs of AI-assisted development (opens elastic.co)

    Elastic Security Labs found that operators behind REF6045, a Mexican banking-fraud campaign, used an LLM to write most of a PowerShell toolkit called SCMBANKER, based on AI-generated code artifacts in the scripts.

    Category
    AI-Enabled
    Attribution
    not-stated, per Elastic Security Labs (confidence not stated)
  48. SysdigVendor report

    JADEPUFFER: Agentic ransomware for automated database extortion (opens sysdig.com)

    Sysdig's Threat Research Team documented what they assess to be the first fully agentic ransomware operation, dubbed JADEPUFFER, where an LLM autonomously gained access via a Langflow RCE flaw, harvested credentials, exploited Nacos authentication bypasses, and encrypted and destroyed a victim's production database for extortion.

    Category
    AI-Enabled
    Malware
    JADEPUFFER
  49. FortiGuard LabsVendor report

    Threat Actors Weaponize AI Hype to Deliver AsyncRAT (opens fortinet.com)

    FortiGuard Labs documented a multi-stage Windows malware campaign using fake AI-themed documents and guides as lures to deliver AsyncRAT via AutoHotkey-based loaders and process hollowing. Chinese-language code artifacts and structured coding style suggest the attackers used generative AI tools to help build the malware, though this is inferred rather than confirmed.

    Category
    AI-Enabled
  50. AnthropicVendor report

    What we learned mapping a year's worth of AI-enabled cyber threats (opens anthropic.com)

    Anthropic analyzed 832 accounts banned for malicious cyber activity between March 2025 and March 2026, mapping their techniques to MITRE ATT&CK. They found AI use shifting from initial access to post-compromise activity, risk scores rising over time, and the framework failing to capture autonomous agentic orchestration seen in a November 2025 state-sponsored espionage case.

    Category
    AI-Enabled
  51. Trend MicroVendor report

    Vibe Hacking: Two AI-Augmented Campaigns Target Government and Financial Sectors in Latin America (opens trendmicro.com)

    Trend Micro identified two campaigns, SHADOW-AETHER-040 and SHADOW-AETHER-064, using agentic AI (including Claude) to drive intrusions from initial access to data exfiltration against government and financial targets in Mexico and Brazil. The AI agents dynamically generated custom tools and backdoors, used jailbreaking via fake red-team pretexts, and integrated with Shodan and VulDB for reconnaissance.

    Category
    AI-Enabled
  52. Gambit SecurityVendor report

    A Single Operator, Two AI Platforms, Nine Government Agencies: The Full Technical Report (opens gambit.security)

    A single threat actor used Anthropic's Claude Code and OpenAI's GPT-4.1 as core operational tools to breach nine Mexican government organizations and exfiltrate hundreds of millions of citizen records between December 2025 and February 2026.

    Category
    AI-Enabled
    Attribution
    Mexico, per Gambit Security (confidence not stated)
  53. IBM X-ForceVendor report

    A Slopoly start to AI-enhanced ransomware attacks (opens ibm.com)

    IBM X-Force found a likely AI-generated PowerShell C2 backdoor, dubbed Slopoly, deployed by ransomware group Hive0163 during a live intrusion using ClickFix, NodeSnake, InterlockRAT and Interlock ransomware. The malware is technically unremarkable but shows guardrail bypass and signals adoption of AI-assisted malware development among established ransomware actors.

    Category
    AI-Enabled
  54. Hunt.io / cyberandramen.netResearch

    LLMs in the Kill Chain: Inside a Custom MCP Targeting FortiGate Devices Across Continents (opens cyberandramen.net)

    A threat actor built a custom MCP server called ARXON that feeds FortiGate reconnaissance data to DeepSeek for attack-plan generation and lets Claude Code autonomously run Impacket, Metasploit and hashcat during live intrusions.

    Category
    AI-Enabled
  55. ESET ResearchVendor report

    PromptSpy ushers in the era of Android threats using GenAI (opens welivesecurity.com)

    ESET found PromptSpy, Android malware that queries Google's Gemini with UI XML dumps to get step-by-step instructions for locking itself into the recent apps list, aiding persistence. The malware also deploys a VNC module for remote device control and targets users in Argentina; no live samples have been seen in telemetry, suggesting it may still be a proof of concept.

    Category
    AI-Enabled
    Attribution
    China, per ESET (medium confidence)
  56. Amazon Threat IntelligenceVendor report

    AI-augmented threat actor accesses FortiGate devices at scale (opens aws.amazon.com)

    A Russian-speaking financially motivated threat actor used multiple commercial generative AI services to plan attacks, generate exploitation scripts and reconnaissance tooling, and automate credential-based compromise of over 600 internet-exposed FortiGate devices across 55+ countries.

    Category
    AI-Enabled
    Actor
    Ed1s0nZ

    Also covered byTeam Cymru

  57. AnthropicVendor report

    Operating Multi-Client Influence Networks Across Platforms (opens cdn.sanity.io)

    Anthropic disrupted an influence-as-a-service operation that used Claude to orchestrate over 100 social media personas across X and Facebook, making tactical engagement decisions and generating image prompts for image-generation models.

    Category
    AI-Enabled
    Malware
    Claude

    Also covered byAnthropic

  58. Google Threat Analysis GroupVendor report

    Google disrupted over 10,000 instances of DRAGONBRIDGE activity in Q1 2024 (opens blog.google)

    Google's TAG reports on DRAGONBRIDGE, a PRC-linked influence operation, disrupting over 10,000 instances in Q1 2024 across YouTube and Blogger, totaling 175,000 lifetime. The actor increasingly used generative AI, including AI-generated news anchors and synthetic voiceovers, to push narratives around Taiwan's election and US social issues, though engagement remained largely inauthentic and low.

    Category
    AI-Enabled
    Attribution
    China, per Google Threat Analysis Group (high confidence)
  59. OpenAIVendor report

    AI and Covert Influence Operations: Latest Trends (opens cdn.openai.com)

    OpenAI describes disrupting five covert influence operations from Russia, China, Iran and an Israeli commercial firm that used its models to generate and refine content, translate text, and fake engagement across social platforms. None of the operations achieved meaningful audience engagement, scoring no higher than Category 2 on the Breakout Scale.

    Category
    AI-Enabled
    Attribution
    Russia, China, Iran, Israel, per OpenAI (confidence not stated)

    Also covered byOpenAI

Added 18 Sep 2026

  1. AnthropicVendor report

    Detecting and countering misuse of AI: September 2026 (opens anthropic.com)

    Anthropic describes actors who automate whole intrusion chains with AI agents. One Russian-speaking espionage operator had agents rebuild malware whenever a security product detected it, and used AI to sort hundreds of gigabytes of stolen data.

    Category
    AI-Enabled
    Marker
    Must-read
    Attribution
    Russia, per Anthropic (confidence not stated)

    Also covered byAnthropic

Added 12 May 2026

  1. Google Threat Intelligence GroupVendor report

    GTIG AI Threat Tracker: Adversaries Leverage AI for Vulnerability Exploitation, Augmented Operations, and Initial Access (opens cloud.google.com)

    GTIG reports adversaries applying AI to vulnerability exploitation, initial access and faster development of evasive, polymorphic malware. It also covers supply chain attacks against AI components, and notes no actor has yet bypassed the core safety logic of frontier models.

    Category
    AI-Enabled
    Marker
    Must-read

Added 25 Feb 2026

  1. OpenAIVendor report

    Disrupting malicious uses of AI (opens openai.com)

    OpenAI's case studies show models used as one step in larger workflows that also rely on websites and social accounts: romance and recovery scams, covert influence operations, and a state-linked harassment effort.

    Category
    AI-Enabled
    Marker
    Must-read
    Actor
    Rybar

    Also covered byHelp Net Security

Added 12 Feb 2026

  1. Google Threat Intelligence GroupVendor report

    GTIG AI Threat Tracker: Distillation, Experimentation, and (Continued) Integration of AI for Adversarial Use (opens cloud.google.com)

    Quarterly view of how actors linked to North Korea, Iran, China and Russia used AI in late 2025. GTIG saw no breakthrough capability, but disrupted frequent model extraction attempts against its own models.

    Category
    AI-Enabled
    Marker
    Must-read
    Attribution
    North Korea, Iran, China, Russia, per Google Threat Intelligence Group (confidence not stated)

    Also covered byGoogle

Added 13 Nov 2025

  1. AnthropicVendor report

    Disrupting the first reported AI-orchestrated cyber espionage campaign (opens anthropic.com)

    A group tasked Claude Code with running intrusions against roughly 30 organisations, with the model carrying out an estimated 80 to 90 percent of tactical work. Anthropic validated a handful of successful compromises before banning the accounts.

    Category
    AI-Enabled
    Marker
    Must-read
    Attribution
    China, per Anthropic (high confidence)

    Also covered byAnthropic

Added 5 Nov 2025

  1. Google Threat Intelligence GroupVendor report

    GTIG AI Threat Tracker: Advances in Threat Actor Usage of AI Tools (opens cloud.google.com)

    GTIG documents the first malware families that query an LLM during execution to generate scripts and rewrite their own code. It also describes actors posing as students or researchers to talk Gemini past its safeguards.

    Category
    AI-Enabled
    Marker
    Must-read
    Actor
    APT28

Added 7 Oct 2025

  1. OpenAIVendor report

    Disrupting malicious uses of AI: October 2025 (opens openai.com)

    OpenAI details banned accounts tied to state actors and criminal groups that used ChatGPT for malware development, scams and surveillance tooling. It reports no evidence that its models gave attackers novel offensive capability.

    Category
    AI-Enabled
    Malware
    XenoRAT

    Also covered byIT BrewOpenAI

Added 23 Sep 2025

  1. DataconomyNews

    SentinelOne finds MalTerminal malware using OpenAI GPT-4 (opens dataconomy.com)

    SentinelLABS hunted for binaries carrying LLM API keys and embedded prompts, and found MalTerminal, which asks GPT-4 to write ransomware or a reverse shell at runtime. A retired API endpoint dates it before November 2023. No live use is known.

    Category
    AI-Enabled

Added 27 Aug 2025

  1. AnthropicVendor report

    Threat Intelligence Report: August 2025 (opens anthropic.com)

    Introduces vibe hacking: one criminal used Claude Code to run data extortion against at least 17 organisations. Other cases cover North Korean remote worker fraud, ransomware sold by a developer with little coding skill, and AI across the fraud ecosystem.

    Category
    AI-Enabled
    Marker
    Must-read
    Attribution
    North Korea, China, per Anthropic (confidence not stated)

    Also covered byAnthropic

Added 26 Aug 2025

  1. ESET ResearchResearch

    First known AI-powered ransomware uncovered by ESET Research (opens welivesecurity.com)

    PromptLock runs OpenAI's gpt-oss-20b locally through Ollama to generate Lua scripts that enumerate, exfiltrate and encrypt files. ESET later confirmed the samples match an academic prototype, not malware deployed in attacks.

    Category
    AI-Enabled
    Malware
    PromptLock

Added 18 Jul 2025

  1. guardsixVendor report

    LAMEHUG: APT28's New Arsenal - First AI-Powered Malware Explained (opens guardsix.com)

    LameHug is Python malware attributed to APT28/UAC-0001 that queries the Qwen 2.5-Coder-32B-Instruct model via the Hugging Face API to dynamically generate Windows recon and data-theft commands from natural language prompts.

    Category
    AI-Enabled
    Attribution
    Russia, per CERT-UA (medium confidence)

    Also covered byThe Hacker News

Added 29 Jan 2025

  1. Google Threat Intelligence GroupVendor report

    Adversarial Misuse of Generative AI (opens cloud.google.com)

    GTIG's first analysis of how government-backed groups used Gemini. Actors from Iran, China, North Korea and Russia used it for research, coding help and content, and did not develop novel capabilities with it.

    Category
    AI-Enabled
    Marker
    Must-read
    Actor
    APT43
    Attribution
    Iran, China, North Korea, Russia, per Google Threat Intelligence Group (confidence not stated)

    Also covered byTechTarget

Added 14 Feb 2024

  1. Microsoft Threat IntelligenceVendor report

    Staying ahead of threat actors in the age of AI (opens microsoft.com)

    Microsoft and OpenAI published the first joint account of state-affiliated groups using LLMs, mostly for reconnaissance, scripting help and social engineering content. The accounts were disabled.

    Category
    AI-Enabled
    Marker
    Must-read
    Attribution
    Russia, North Korea, Iran, China, per Microsoft (confidence not stated)

    Also covered byOpenAI