

 Sekoia
 Anthropic

 RailwayVendor report
Incident Report: October 21st Security Attack (opens blog.railway.com)
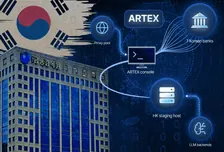
Railway reports an intrusion in which the attacker used AI agent fanouts, reportedly abliterated models in an ARTEX-like harness per Wiz, to find exploits and move laterally. They stole and decrypted environment variables, mainly AI provider keys, from up to 1.85% of workspaces. Estimated unauthorized spend on the stolen keys was about $740,000.
- Category
- AI-Enabled
 Okta Threat Intelligence
 GitGuardian
 Datadog Security Labs
 CERT-EU
 The Hacker News
 Malbear Labs
 Microsoft Security Blog
 GitHub (Arcanum-Sec)
 Hunt.io
 Censys
 404 Media
 Check Point Research

 Acronis Threat Research Unit

 Bitdefender
 Binance
 Nextron Systems
 Unit 42
 RST Cloud
 Google Threat Intelligence Group
 Profero
 Cisco Talos
 Sophos
 Zimperium
 CrowdStrike
 Group-IB

 SecurityWeek
 ASEC
 Plaintext
 SOCRadar
 Trend Micro

 Help Net Security
 Flare
 Cohere
 BlackFog
 AI Security Institute

 Zscaler ThreatLabz
 Straiker

 Wiz
 Huntress
 LiteLLM
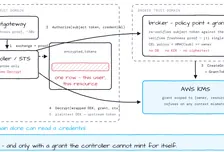
 agentgateway
 JPCERT/CC
 Check Point Research
 NorForge
 Forescout
 Previdian
 Security Affairs
 Signals Corps
 Team Cymru
 AIR Security
 The Record
 ReliaQuest
 Genians
 The Register
 Zenity Labs
 rogueauthority.org
 Spectrum Security
 Black Lotus Labs (Lumen)
 CyberScoop
 Hudson Rock
 Gen Digital
 Wikimedia Foundation
 BleepingComputer

 arXiv
 Abstract Security
 Cleafy
 Krebs on Security
 Transluce
 ThreatDown
 Socket

 SpyCloud
 Gambit Security
 SentinelOne
 heyitsas.im
 Cyber Insurance News
 GreyNoise
 CNN
 Malwarebytes
 Unit 42
 Cyera
 SpecterOps
 Tel Aviv University
 Moonlock
 Permiso
 Trend Micro
 Cloud Security Alliance
 Google
 Abnormal AI
 Resecurity
 Netskope
 Volexity

 EclecticIQ
 Knostic
 The CyberWire
 Recorded Future
 LevelBlue (SpiderLabs)
 Netenrich

 Snyk
 Pillar Security
 Trail of Bits

 Hugging Face
 Elastic Security Labs
 Sysdig

 Breached.company
 IBM X-Force
 Hunt.io / cyberandramen.net
 Amazon Threat Intelligence
 OWASP GenAI Security Project
 Infosecurity Magazine
 IT Brew
 Koi Security
 Dark Reading
 Dataconomy
 guardsix
 TechTarget